Capabilities
Access & Governance
Access is checked by the application for the person, workspace, site and requested action.
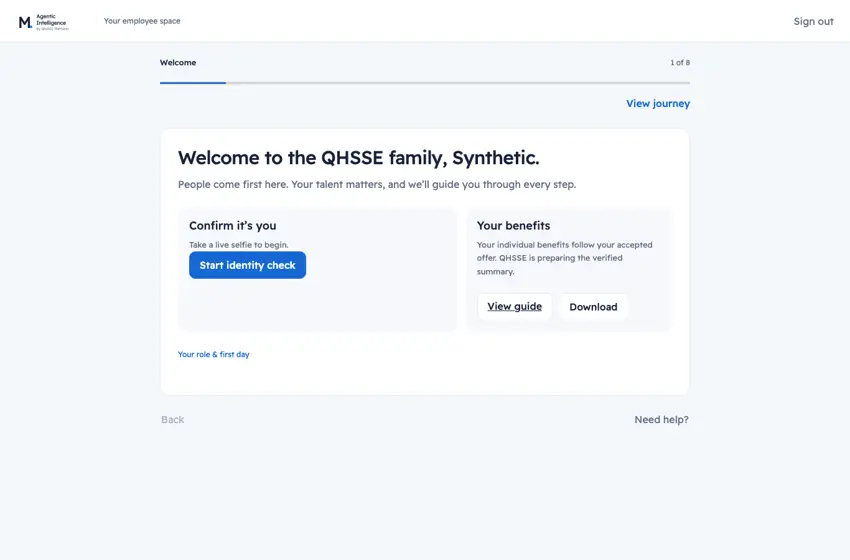
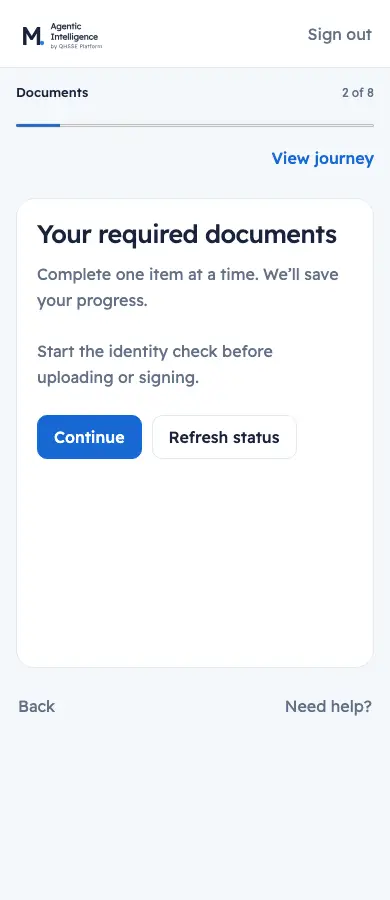
People before access.
Identity and authorized workspace entry remain controlled.
Saved acceptance screenshot · Synthetic employee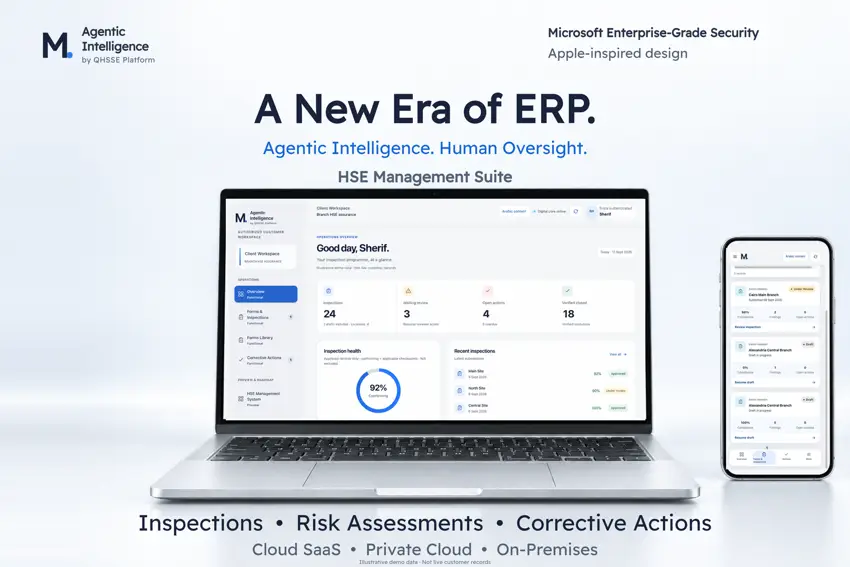
A governed shared foundation.
Public product imagery does not grant module access.
Existing approved ERP brand cover · Illustrative demo; depicted hosting/security wording is historical brand copy, not release certification.The right work. The right person.
Provider-approved module access is the upper limit for every account. Workspace roles determine actions inside that limit; the application also checks sites and records.
- Only authorized Platform Administrators grant module access.
- Customer admins work within provider limits.
- Role changes cannot expand module ceilings.
- Workspace, site, record and action checks remain enforced.
Keep exploring.
Agentic Customization
Your bottleneck. Our next breakthrough.
Tell us what slows your business down. Get a tailored solution proposal and estimated cost within 24 hours.